Become the security engineer companies fight to hire.
Build sharper security instincts through safe, focused practice missions spanning web and API security, cloud and Kubernetes, network and Active Directory, digital forensics, AI and agent security, and interview prep.
Play a real mission in your browser without creating an account.
Or get early access by email
Not ready to jump in? Leave your email and we'll let you know when new access opens.
By joining you agree to our Terms and Privacy Policy.
Built by security engineers who've sat on both sides of the interview table.
See it before you sign up
Watch a real mission run, right here.
This is the actual Insecure Login mission, replayed as a scripted preview. Play the live version yourself in the box below.
Real mission, scripted preview. Insecure Login above plays fully interactive when you open it.
10
practice domains
5-15 min
mission format
3-part
daily skill stack
Safe
simulated scenarios
Team
readiness view
The honest problem
The gap between learning and doing is enormous.
Knowing a term is not the same as recognizing a weak control, choosing the next investigative step, or explaining the risk under pressure.
Courses explain the concept
But recognition still feels difficult when the signal is buried in code, logs, or system state.
Quizzes reward recall
But security work depends on choosing what to inspect next and defending that decision.
Labs can demand setup
A long toolchain makes it harder to build a consistent practice habit around a busy week.
Insecure Login
Web Application · Easy · 40 XP
Mission brief
Find the exposed credential.
Review the sample login handler and identify the line containing the primary vulnerability.
- 1Inspect app.js
- 2Select the vulnerable line
- 3Submit the finding
$ cat app.js
1 function login(user, pass) {
2 const SECRET = "admin123";
3 if (pass === SECRET) return true;
4 return false;
5 }
$ select line
What makes SecMissions different
Eight things that work better together.
Most training solves one piece of the puzzle. SecMissions connects practice, explanation, and repeatable momentum.
Browser-based missions
Open a focused scenario, inspect the evidence, and make the call without configuring a VM.
rq launch mission
ready in browser
No setup · Safe sandbox
Structured security domains
Move across 10 security domains, then go deeper with 11 advanced tracks covering offensive cloud, network and Active Directory, digital forensics, and AI and agent security.
Breadth without drift
Adaptive interview lab
Turn technical findings into crisp answers about evidence, impact, remediation, and tradeoffs.
Rehearse the room
XP and streak loop
A small daily stack, streak protection, and useful unlocks make practice worth returning to without turning it into anxiety.
Streak protected · badge unlocked
Healthy momentum
Skill passport
Show retained skill by domain, mission evidence, interview explanations, and a verifiable certificate of completion for each finished training path.
Proof from work
Safe synthetic scenarios
Practice realistic security judgment inside contained missions designed for authorized learning.
Authorized education only
In-browser Python lab
Real interview-style problems, graded by hidden tests that run entirely in your browser through Pyodide.
$ python3 solve.py
3 / 3 hidden tests passed
Nothing leaves your device
Red-team network simulation
Scan, enumerate, and escalate across a simulated multi-host network, with each step gated on the evidence you actually found.
Contained and authorized
Why people come back daily
Built for the dopamine loop.
Security practice is hard. SecMissions makes the next step visible, rewarding, and small enough to repeat.
- 1
Start a focused mission
A short brief and browser sandbox create immediate tension without setup.
tension builds - 2
Inspect the evidence
Read code, logs, cloud state, or terminal output until the strongest signal appears.
signal found - 3
Submit the finding
Commit to the risk, impact, and defensive action instead of passively reading a solution.
+80-180 XP - 4
Unlock the walkthrough
Review the attacker path, defender lesson, and concise prevention pattern.
understanding secured - 5
Keep the streak alive
Return for one mission tomorrow and the next useful challenge is already waiting.
streak active
Current tier
Security Reasoning · Specialist
5 days
Current streak
Next unlock
Interview drill opens after this path
Finish a training path to earn a shareable certificate of completion, and opt into the cohort or global leaderboard to see how consistent practice compares.
Built to compete
A daily readiness layer for staying sharp.
HTB and TryHackMe are strong places to learn and explore. SecMissions is positioned around a different buyer need: keep security judgment sharp, measurable, and easy to repeat during a normal work week.
SecMissions is the cyber skills gym: five-minute missions that build and prove security judgment.
Daily adaptive practice
A quick win, weak-skill rep, and focused daily practice make the next session obvious.
Remixed scenarios
Changing evidence prevents answer memorization and trains pattern recognition.
Team readiness
Managers see coverage, decay, cohorts, and drill outcomes instead of raw course completion.
Verified skill passport
Learners can prove how they reasoned, explained, and improved under pressure.
Enough reading. Solve one now.
Pick a real mission and try it free in your browser. No account, no setup, just the evidence and a decision to defend.
Try a mission - freePractice across the role
10 security domains. One structured practice system.
Build breadth across the real SecMissions catalog without losing sight of the next useful mission.
Start with a free Web, Cloud, or code-review mission, then expand across the full catalog.
Explore free missionsExplore by job role
Aiming for a specific title? Start directly from the role.
10 real job titles, each mapped to a starter mission plan and an honest coverage score.
The differentiator
Practice explaining your reasoning out loud.
Clearing a mission is only half the skill. Interview Lab helps you rehearse the explanation: what you saw, why it matters, what you would verify, and how you would fix it.
Adaptive follow-ups: Move beyond a surface answer and probe the assumptions underneath it.
Both sides of the attack: Practice both prevention and detection for each vulnerability class.
Written debrief: Review clarity, depth, assumptions, and prioritization after each session.
Connected practice: Use recent missions as the source material for explanation drills.
Mock Interview
AppSec engineer · illustrative practice session
Structured feedback
8.4 / 10Strong impact framing. Next, name the telemetry you would inspect and separate short-term containment from long-term remediation.
Where interviews are actually lost
Knowing the fix is not the same as explaining it under pressure.
Most candidates can spot the bug. Fewer can walk an interviewer through the evidence, the impact, and the fix out loud without losing the thread. Here is the shape of an Interview Lab session, sped up.
Interviewer asks
An EDR alert fires: Outlook spawned an encoded PowerShell child process on a finance workstation, followed by one outbound connection to a rarely seen destination. Walk me through it.
Alert summary
host: FIN-WKS-042
parent: outlook.exe
child: powershell.exe -enc SQBFAFgA...
network: 1 outbound connection, rare destination
Structured feedback
91 / 100- Cites the specific evidence behind the alert
- Explains why the parent process matters
- Names a concrete containment step
- States the tradeoff plainly
Scripted preview of the Interview Lab. Fictional example question, written for this demo.
Interview Lab covers every domain in the catalog, with adaptive follow-ups and written feedback after each session.
Proof from practice
A skill profile built from completed work.
Certificates say you showed up. SecMissions is designed to show what you practiced: missions completed, domains growing, explanations rehearsed, and gaps to revisit.
SecMissions skill profile
Career track · illustrative learner view
Mission history
Completed work
Debriefs
Reasoning review
Interview Lab
Explanation practice
Everywhere you already are
One skill.
Every screen.
Open a mission on your phone between meetings. Pick up the proxy workbench on your laptop tonight. It is the same account and the same progress everywhere.
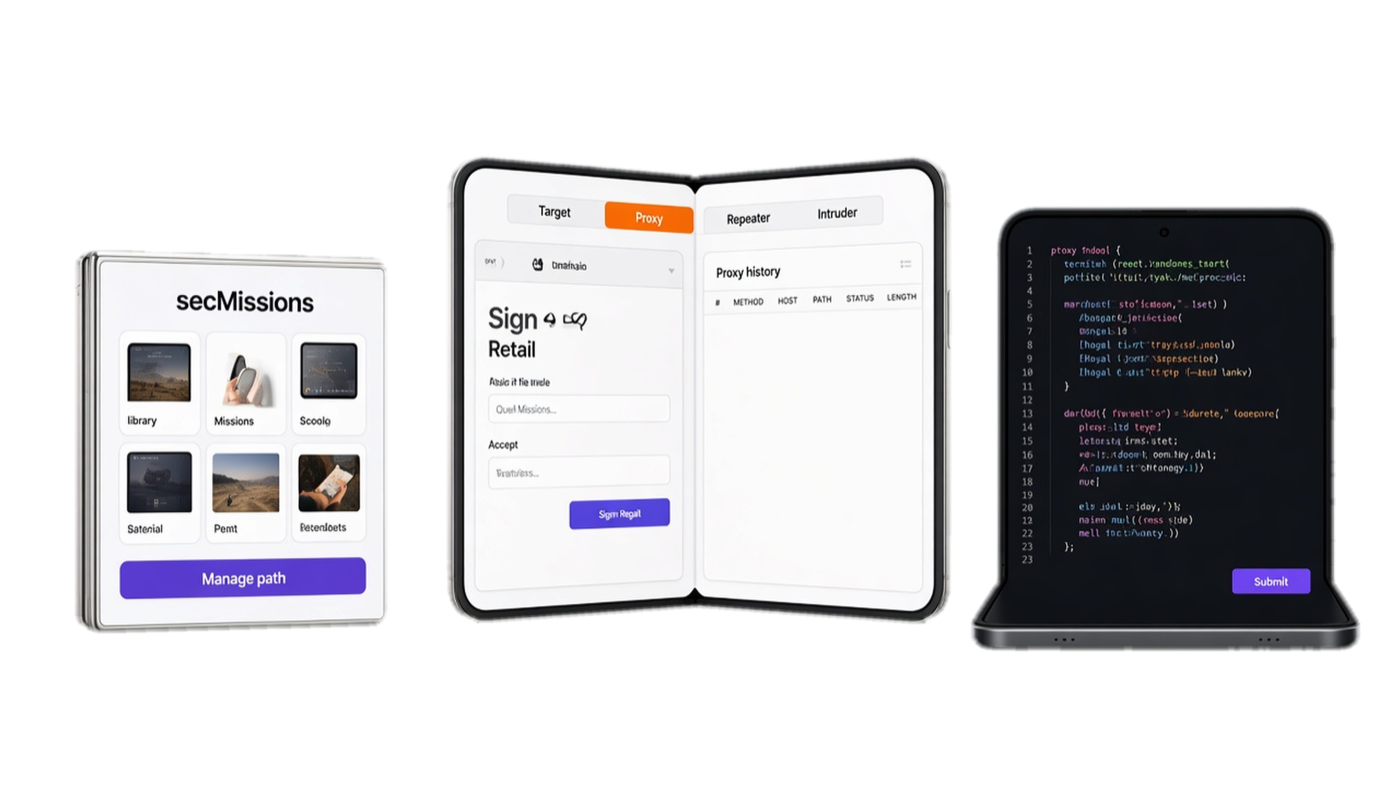
- Any modern browser
- No VPN, no virtual machine, no admin rights. It runs on a locked down work laptop.
- Install it like an app
- Add SecMissions to your home screen and finish a two minute drill while you wait for coffee.
- Progress follows you
- The same account, streak, and mission history sync the moment you sign in on a new device.
Pricing, in public
Start free. One yearly plan for everything else.
Pricing locks in at launch: join the waitlist for founding-member rates. Checkout is not connected yet, so every button below records which plan you want rather than charging you.
Free
$0
forever
For building the habit, and the whole entry-level path for new grads and career changers.
- One daily mission, every day
- Junior Launchpad round: the entry-level interview round, always free in full and rotates daily
- A daily taste of every other Interview Lab round, plus every question you unlock by completing missions
Pro
$149
per year
Founding member: $99 per year before launch
For everything an individual learner needs, all year.
- The complete mission library, every domain
- Full Interview Lab with explanation scoring
- Readiness passport with evidence you can share
Interview Sprint
$79
one time, 30 days
For candidates with an interview already on the calendar.
- 30 days of full access, no subscription
- Interview Lab and every interview-prep hub
- A paced 30-day plan built around your target role
Teams & EDU
$995
per cohort
For universities, bootcamps, and security teams.
- Up to 40 seats in a private cohort
- Instructor dashboard with coverage and skill-gap views
- Assignable mission sets and weekly readiness drills
New grad or career changer? The daily Junior Launchpad round is free forever, in full, and hello@secmissions.com sends a free full-access coupon for your first security-role search.
Your next study session can be a mission.
Join early access for practical cyber reasoning, visible progress, and safe simulated training.
For authorized and ethical security education only.